AzerothCore 3.3.5a
OpenSource WoW Emulator
Loading...
Searching...
No Matches
AuthSession Class Referencefinal

#include "AuthSession.h"

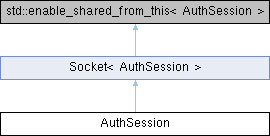
Inheritance diagram for AuthSession:
Socket< AuthSession >

Public Member Functions

 AuthSession (IoContextTcpSocket &&socket)
 
void Start () override
 
bool Update () final
 
void SendPacket (ByteBuffer &packet)
 
- Public Member Functions inherited from Socket< AuthSession >
 Socket (IoContextTcpSocket &&socket)
 
virtual ~Socket ()
 
boost::asio::ip::address GetRemoteIpAddress () const
 
uint16 GetRemotePort () const
 
void AsyncRead ()
 
void AsyncReadProxyHeader ()
 
void AsyncReadWithCallback (void(T::*callback)(boost::system::error_code, std::size_t))
 
void QueuePacket (MessageBuffer &&buffer)
 
ProxyHeaderReadingState GetProxyHeaderReadingState () const
 
bool IsOpen () const
 
void CloseSocket ()
 
void DelayedCloseSocket ()
 Marks the socket for closing after write buffer becomes empty.
 
MessageBuffer & GetReadBuffer ()
 

Static Public Member Functions

static std::unordered_map< uint8, AuthHandler > InitHandlers ()
 

Protected Member Functions

SocketReadCallbackResult ReadHandler () final
 
- Protected Member Functions inherited from Socket< AuthSession >
virtual void OnClose ()
 
bool AsyncProcessQueue ()
 
void SetNoDelay (bool enable)
 

Private Types

typedef Socket< AuthSession > AuthSocket
 

Private Member Functions

bool HandleLogonChallenge ()
 
bool HandleLogonProof ()
 
bool HandleReconnectChallenge ()
 
bool HandleReconnectProof ()
 
bool HandleRealmList ()
 
void CheckIpCallback (PreparedQueryResult result)
 
void LogonChallengeCallback (PreparedQueryResult result)
 
void ReconnectChallengeCallback (PreparedQueryResult result)
 
void RealmListCallback (PreparedQueryResult result)
 
bool VerifyVersion (uint8 const *a, int32 aLength, Acore::Crypto::SHA1::Digest const &versionProof, bool isReconnect)
 

Private Attributes

Optional< Acore::Crypto::SRP6 > _srp6
 
SessionKey _sessionKey = {}
 
std::array< uint8, 16 > _reconnectProof = {}
 
AuthStatus _status
 
AccountInfo _accountInfo
 
Optional< std::vector< uint8 > > _totpSecret
 
std::string _localizationName
 
std::string _os
 
std::string _ipCountry
 
uint16 _build
 
uint8 _expversion
 
QueryCallbackProcessor _queryProcessor
 

Detailed Description

Member Typedef Documentation

◆ AuthSocket

Constructor & Destructor Documentation

◆ AuthSession()

AuthSession::AuthSession ( IoContextTcpSocket &&  socket)
168 :
169 Socket(std::move(socket)), _status(STATUS_CHALLENGE), _build(0), _expversion(0) { }
@ STATUS_CHALLENGE
Definition AuthSession.h:39
AuthStatus _status
Definition AuthSession.h:99
uint16 _build
Definition AuthSession.h:105
uint8 _expversion
Definition AuthSession.h:106
Definition Socket.h:68

Member Function Documentation

◆ CheckIpCallback()

void AuthSession::CheckIpCallback ( PreparedQueryResult  result)
private
193{
194 if (result)
195 {
196 bool banned = false;
197
198 for (auto const& fields : *result)
199 {
200 if (fields[0].Get<uint64>() != 0)
201 {
202 banned = true;
203 break;
204 }
205 }
206
207 if (banned)
208 {
209 ByteBuffer pkt;
211 pkt << uint8(0x00);
212 pkt << uint8(WOW_FAIL_BANNED);
213 SendPacket(pkt);
214 LOG_DEBUG("session", "[AuthSession::CheckIpCallback] Banned ip '{}:{}' tries to login!", GetRemoteIpAddress().to_string(), GetRemotePort());
215 return;
216 }
217 }
218
219 AsyncRead();
220}
@ WOW_FAIL_BANNED
Definition AuthCodes.h:26
@ AUTH_LOGON_CHALLENGE
Definition AuthSession.cpp:41
std::uint8_t uint8
Definition Define.h:109
#define LOG_DEBUG(filterType__,...)
Definition Log.h:157
void SendPacket(ByteBuffer &packet)
Definition AuthSession.cpp:273
Definition ByteBuffer.h:70
boost::asio::ip::address GetRemoteIpAddress() const
Definition Socket.h:107
uint16 GetRemotePort() const
Definition Socket.h:112
void AsyncRead()
Definition Socket.h:117

References Socket< AuthSession >::AsyncRead(), AUTH_LOGON_CHALLENGE, Socket< AuthSession >::GetRemoteIpAddress(), Socket< AuthSession >::GetRemotePort(), LOG_DEBUG, SendPacket(), and WOW_FAIL_BANNED.

Referenced by Start().

◆ HandleLogonChallenge()

bool AuthSession::HandleLogonChallenge ( )
private
287{
289
290 sAuthLogonChallenge_C* challenge = reinterpret_cast<sAuthLogonChallenge_C*>(GetReadBuffer().GetReadPointer());
291 if (challenge->size - (sizeof(sAuthLogonChallenge_C) - AUTH_LOGON_CHALLENGE_INITIAL_SIZE - 1) != challenge->I_len)
292 return false;
293
294 std::string login((char const*)challenge->I, challenge->I_len);
295 LOG_DEBUG("server.authserver", "[AuthChallenge] '{}'", login);
296
297 _build = challenge->build;
299 std::array<char, 5> os;
300 os.fill('\0');
301 memcpy(os.data(), challenge->os, sizeof(challenge->os));
302 _os = os.data();
303
304 // Restore string order as its byte order is reversed
305 std::reverse(_os.begin(), _os.end());
306
307 _localizationName.resize(4);
308 for (int i = 0; i < 4; ++i)
309 _localizationName[i] = challenge->country[4 - i - 1];
310
311 // Written to account.locale in the same update as the session key: non-text bytes would fail the login
312 auto isLetter = [](unsigned char c) { return std::isalpha(c); };
313 if (!std::all_of(_localizationName.begin(), _localizationName.end(), isLetter))
315
316 // Get the account details from the account table
318 stmt->SetData(0, GetRemoteIpAddress().to_string());
319 stmt->SetData(1, login);
320
321 _queryProcessor.AddCallback(LoginDatabase.AsyncQuery(stmt).WithPreparedCallback(std::bind(&AuthSession::LogonChallengeCallback, this, std::placeholders::_1)));
322 return true;
323}
@ POST_BC_EXP_FLAG
Definition AuthCodes.h:76
@ NO_VALID_EXP_FLAG
Definition AuthCodes.h:78
@ PRE_BC_EXP_FLAG
Definition AuthCodes.h:77
#define AUTH_LOGON_CHALLENGE_INITIAL_SIZE
Definition AuthSession.cpp:121
@ STATUS_CLOSED
Definition AuthSession.h:44
char const * localeNames[TOTAL_LOCALES]
Definition Common.cpp:20
#define DEFAULT_LOCALE
Definition Common.h:140
DatabaseWorkerPool< LoginDatabaseConnection > LoginDatabase
Accessor to the realm/login database.
Definition DatabaseEnv.cpp:22
@ LOGIN_SEL_LOGONCHALLENGE
Definition LoginDatabase.h:44
T & AddCallback(T &&query)
Definition AsyncCallbackProcessor.h:34
std::string _os
Definition AuthSession.h:103
QueryCallbackProcessor _queryProcessor
Definition AuthSession.h:108
void LogonChallengeCallback(PreparedQueryResult result)
Definition AuthSession.cpp:325
std::string _localizationName
Definition AuthSession.h:102
uint8 * GetReadPointer()
Definition MessageBuffer.h:58
Acore::Types::is_default< T > SetData(const uint8 index, T value)
Definition PreparedStatement.h:77
Definition PreparedStatement.h:157
MessageBuffer & GetReadBuffer()
Definition Socket.h:200
Definition AuthCodes.cpp:22
bool IsPreBCAcceptedClientBuild(uint32 build)
Definition AuthCodes.cpp:25
bool IsPostBCAcceptedClientBuild(uint32 build)
Definition AuthCodes.cpp:30
Definition AuthSession.cpp:56
uint8 I[1]
Definition AuthSession.cpp:71
uint16 build
Definition AuthSession.cpp:64
uint8 country[4]
Definition AuthSession.cpp:67
uint8 I_len
Definition AuthSession.cpp:70
uint16 size
Definition AuthSession.cpp:59
uint8 os[4]
Definition AuthSession.cpp:66

References _build, _expversion, _localizationName, _os, _queryProcessor, _status, AsyncCallbackProcessor< T >::AddCallback(), AUTH_LOGON_CHALLENGE_INITIAL_SIZE, AUTH_LOGON_CHALLENGE_C::build, AUTH_LOGON_CHALLENGE_C::country, DEFAULT_LOCALE, Socket< AuthSession >::GetReadBuffer(), MessageBuffer::GetReadPointer(), Socket< AuthSession >::GetRemoteIpAddress(), AUTH_LOGON_CHALLENGE_C::I, AUTH_LOGON_CHALLENGE_C::I_len, AuthHelper::IsPostBCAcceptedClientBuild(), AuthHelper::IsPreBCAcceptedClientBuild(), localeNames, LOG_DEBUG, LOGIN_SEL_LOGONCHALLENGE, LoginDatabase, LogonChallengeCallback(), NO_VALID_EXP_FLAG, AUTH_LOGON_CHALLENGE_C::os, POST_BC_EXP_FLAG, PRE_BC_EXP_FLAG, PreparedStatementBase::SetData(), AUTH_LOGON_CHALLENGE_C::size, and STATUS_CLOSED.

Referenced by InitHandlers().

◆ HandleLogonProof()

bool AuthSession::HandleLogonProof ( )
private
465{
466 LOG_DEBUG("server.authserver", "Entering _HandleLogonProof");
468
469 // Read the packet
470 sAuthLogonProof_C* logonProof = reinterpret_cast<sAuthLogonProof_C*>(GetReadBuffer().GetReadPointer());
471
472 // If the client has no valid version
474 {
475 // Check if we have the appropriate patch on the disk
476 LOG_DEBUG("network", "Client with invalid version, patching is not implemented");
477 return false;
478 }
479
480 // Check if SRP6 results match (password is correct), else send an error
481 if (Optional<SessionKey> K = _srp6->VerifyChallengeResponse(logonProof->A, logonProof->clientM))
482 {
483 _sessionKey = *K;
484 // Check auth token
485 bool tokenSuccess = false;
486 bool sentToken = (logonProof->securityFlags & 0x04);
487 if (sentToken && _totpSecret)
488 {
489 uint8 size = *(GetReadBuffer().GetReadPointer() + sizeof(sAuthLogonProof_C));
490 std::string token(reinterpret_cast<char*>(GetReadBuffer().GetReadPointer() + sizeof(sAuthLogonProof_C) + sizeof(size)), size);
491 GetReadBuffer().ReadCompleted(sizeof(size) + size);
492
493 uint32 incomingToken = *Acore::StringTo<uint32>(token);
494 tokenSuccess = Acore::Crypto::TOTP::ValidateToken(*_totpSecret, incomingToken);
495 memset(_totpSecret->data(), 0, _totpSecret->size());
496 }
497 else if (!sentToken && !_totpSecret)
498 tokenSuccess = true;
499
500 if (!tokenSuccess)
501 {
502 ByteBuffer packet;
503 packet << uint8(AUTH_LOGON_PROOF);
505 packet << uint16(0); // LoginFlags, 1 has account message
506 SendPacket(packet);
507 return true;
508 }
509
510 if (!VerifyVersion(logonProof->A.data(), logonProof->A.size(), logonProof->crc_hash, false))
511 {
512 ByteBuffer packet;
513 packet << uint8(AUTH_LOGON_PROOF);
515 SendPacket(packet);
516 return true;
517 }
518
519 LOG_DEBUG("server.authserver", "'{}:{}' User '{}' successfully authenticated", GetRemoteIpAddress().to_string(), GetRemotePort(), _accountInfo.Login);
520
521 // Update the sessionkey, last_ip, last login time and reset number of failed logins in the account table for this account
522 // No SQL injection (escaped user name) and IP address as received by socket
523
524 std::string address = sConfigMgr->GetOption<bool>("AllowLoggingIPAddressesInDatabase", true, true) ? GetRemoteIpAddress().to_string() : "0.0.0.0";
526 stmt->SetData(0, _sessionKey);
527 stmt->SetData(1, address);
528 stmt->SetData(2, _localizationName);
529 stmt->SetData(3, _os);
530 stmt->SetData(4, _accountInfo.Login);
532 .WithPreparedCallback([this, M2 = Acore::Crypto::SRP6::GetSessionVerifier(logonProof->A, logonProof->clientM, _sessionKey)](PreparedQueryResult const&)
533 {
534 // Finish SRP6 and send the final result to the client
535 ByteBuffer packet;
536 if (_expversion & POST_BC_EXP_FLAG) // 2.x and 3.x clients
537 {
538 sAuthLogonProof_S proof;
539 proof.M2 = M2;
540 proof.cmd = AUTH_LOGON_PROOF;
541 proof.error = 0;
542 proof.AccountFlags = _accountInfo.Flags;
543 proof.SurveyId = 0;
544 proof.LoginFlags = 0; // 0x1 = has account message
545
546 packet.resize(sizeof(proof));
547 std::memcpy(packet.contents(), &proof, sizeof(proof));
548 }
549 else
550 {
551 sAuthLogonProof_S_Old proof;
552 proof.M2 = M2;
553 proof.cmd = AUTH_LOGON_PROOF;
554 proof.error = 0;
555 proof.unk2 = 0x00;
556
557 packet.resize(sizeof(proof));
558 std::memcpy(packet.contents(), &proof, sizeof(proof));
559 }
560
561 SendPacket(packet);
563 }));
564 }
565 else
566 {
567 ByteBuffer packet;
568 packet << uint8(AUTH_LOGON_PROOF);
570 packet << uint16(0); // LoginFlags, 1 has account message
571 SendPacket(packet);
572
573 LOG_INFO("server.authserver.hack", "'{}:{}' [AuthChallenge] account {} tried to login with invalid password!",
575
576 uint32 MaxWrongPassCount = sConfigMgr->GetOption<int32>("WrongPass.MaxCount", 0);
577
578 // We can not include the failed account login hook. However, this is a workaround to still log this.
579 if (sConfigMgr->GetOption<bool>("WrongPass.Logging", false))
580 {
582 logstmt->SetData(0, _accountInfo.Id);
583 logstmt->SetData(1, GetRemoteIpAddress().to_string());
584 logstmt->SetData(2, "Login to WoW Failed - Incorrect Password");
585
586 LoginDatabase.Execute(logstmt);
587 }
588
589 if (MaxWrongPassCount > 0)
590 {
591 //Increment number of failed logins by one and if it reaches the limit temporarily ban that account or IP
593 stmt->SetData(0, _accountInfo.Login);
594 LoginDatabase.Execute(stmt);
595
596 if (++_accountInfo.FailedLogins >= MaxWrongPassCount)
597 {
598 uint32 WrongPassBanTime = sConfigMgr->GetOption<int32>("WrongPass.BanTime", 600);
599 bool WrongPassBanType = sConfigMgr->GetOption<bool>("WrongPass.BanType", false);
600
601 if (WrongPassBanType)
602 {
603 stmt = LoginDatabase.GetPreparedStatement(LOGIN_INS_ACCOUNT_AUTO_BANNED);
604 stmt->SetData(0, _accountInfo.Id);
605 stmt->SetData(1, WrongPassBanTime);
606 LoginDatabase.Execute(stmt);
607
608 LOG_DEBUG("server.authserver", "'{}:{}' [AuthChallenge] account {} got banned for '{}' seconds because it failed to authenticate '{}' times",
609 GetRemoteIpAddress().to_string(), GetRemotePort(), _accountInfo.Login, WrongPassBanTime, _accountInfo.FailedLogins);
610 }
611 else
612 {
613 stmt = LoginDatabase.GetPreparedStatement(LOGIN_INS_IP_AUTO_BANNED);
614 stmt->SetData(0, GetRemoteIpAddress().to_string());
615 stmt->SetData(1, WrongPassBanTime);
616 LoginDatabase.Execute(stmt);
617
618 LOG_DEBUG("server.authserver", "'{}:{}' [AuthChallenge] IP got banned for '{}' seconds because account {} failed to authenticate '{}' times",
619 GetRemoteIpAddress().to_string(), GetRemotePort(), WrongPassBanTime, _accountInfo.Login, _accountInfo.FailedLogins);
620 }
621 }
622 }
623 }
624
625 return true;
626}
@ WOW_FAIL_UNKNOWN_ACCOUNT
Definition AuthCodes.h:27
@ WOW_FAIL_VERSION_INVALID
Definition AuthCodes.h:32
@ AUTH_LOGON_PROOF
Definition AuthSession.cpp:42
struct AUTH_LOGON_PROOF_C sAuthLogonProof_C
@ STATUS_AUTHED
Definition AuthSession.h:42
std::shared_ptr< PreparedResultSet > PreparedQueryResult
Definition DatabaseEnvFwd.h:45
std::int32_t int32
Definition Define.h:103
std::uint32_t uint32
Definition Define.h:107
std::uint16_t uint16
Definition Define.h:108
#define LOG_INFO(filterType__,...)
Definition Log.h:153
@ LOGIN_INS_ACCOUNT_AUTO_BANNED
Definition LoginDatabase.h:40
@ LOGIN_INS_FALP_IP_LOGGING
Definition LoginDatabase.h:122
@ LOGIN_UPD_LOGONPROOF
Definition LoginDatabase.h:43
@ LOGIN_UPD_FAILEDLOGINS
Definition LoginDatabase.h:46
@ LOGIN_INS_IP_AUTO_BANNED
Definition LoginDatabase.h:36
std::optional< T > Optional
Optional helper class to wrap optional values within.
Definition Optional.h:24
static SHA1::Digest GetSessionVerifier(EphemeralKey const &A, SHA1::Digest const &clientM, SessionKey const &K)
Definition SRP6.h:52
Optional< Acore::Crypto::SRP6 > _srp6
Definition AuthSession.h:95
SessionKey _sessionKey
Definition AuthSession.h:96
AccountInfo _accountInfo
Definition AuthSession.h:100
bool VerifyVersion(uint8 const *a, int32 aLength, Acore::Crypto::SHA1::Digest const &versionProof, bool isReconnect)
Definition AuthSession.cpp:848
Optional< std::vector< uint8 > > _totpSecret
Definition AuthSession.h:101
void ReadCompleted(size_type bytes)
Definition MessageBuffer.h:61
#define sConfigMgr
Definition Config.h:93
Definition AuthSession.cpp:76
Acore::Crypto::SHA1::Digest clientM
Definition AuthSession.cpp:79
Acore::Crypto::SRP6::EphemeralKey A
Definition AuthSession.cpp:78
uint8 securityFlags
Definition AuthSession.cpp:82
Acore::Crypto::SHA1::Digest crc_hash
Definition AuthSession.cpp:80
uint32 FailedLogins
Definition AuthSession.h:58
uint32 Id
Definition AuthSession.h:52
std::string Login
Definition AuthSession.h:53
static bool ValidateToken(Secret const &key, uint32 token)
Definition TOTP.cpp:44

References _accountInfo, _expversion, _localizationName, _os, _queryProcessor, _sessionKey, _srp6, _status, _totpSecret, AUTH_LOGON_PROOF_C::A, AsyncCallbackProcessor< T >::AddCallback(), AUTH_LOGON_PROOF, AUTH_LOGON_PROOF_C::clientM, AUTH_LOGON_PROOF_C::crc_hash, Socket< AuthSession >::GetReadBuffer(), MessageBuffer::GetReadPointer(), Socket< AuthSession >::GetRemoteIpAddress(), Socket< AuthSession >::GetRemotePort(), Acore::Crypto::SRP6::GetSessionVerifier(), LOG_DEBUG, AccountInfo::Login, LOGIN_UPD_LOGONPROOF, LoginDatabase, NO_VALID_EXP_FLAG, MessageBuffer::ReadCompleted(), sConfigMgr, AUTH_LOGON_PROOF_C::securityFlags, SendPacket(), PreparedStatementBase::SetData(), STATUS_AUTHED, STATUS_CLOSED, Acore::Crypto::TOTP::ValidateToken(), VerifyVersion(), WOW_FAIL_UNKNOWN_ACCOUNT, and WOW_FAIL_VERSION_INVALID.

Referenced by InitHandlers().

◆ HandleRealmList()

bool AuthSession::HandleRealmList ( )
private
735{
736 LOG_DEBUG("server.authserver", "Entering _HandleRealmList");
737
739 stmt->SetData(0, _accountInfo.Id);
740
741 _queryProcessor.AddCallback(LoginDatabase.AsyncQuery(stmt).WithPreparedCallback(std::bind(&AuthSession::RealmListCallback, this, std::placeholders::_1)));
743 return true;
744}
@ STATUS_WAITING_FOR_REALM_LIST
Definition AuthSession.h:43
@ LOGIN_SEL_REALM_CHARACTER_COUNTS
Definition LoginDatabase.h:53
void RealmListCallback(PreparedQueryResult result)
Definition AuthSession.cpp:746

References _accountInfo, _queryProcessor, _status, AsyncCallbackProcessor< T >::AddCallback(), AccountInfo::Id, LOG_DEBUG, LOGIN_SEL_REALM_CHARACTER_COUNTS, LoginDatabase, RealmListCallback(), PreparedStatementBase::SetData(), and STATUS_WAITING_FOR_REALM_LIST.

Referenced by InitHandlers().

◆ HandleReconnectChallenge()

bool AuthSession::HandleReconnectChallenge ( )
private
629{
631
632 sAuthLogonChallenge_C* challenge = reinterpret_cast<sAuthLogonChallenge_C*>(GetReadBuffer().GetReadPointer());
633 if (challenge->size - (sizeof(sAuthLogonChallenge_C) - AUTH_LOGON_CHALLENGE_INITIAL_SIZE - 1) != challenge->I_len)
634 return false;
635
636 std::string login((char const*)challenge->I, challenge->I_len);
637 LOG_DEBUG("server.authserver", "[ReconnectChallenge] '{}'", login);
638
639 _build = challenge->build;
641
642 std::array<char, 5> os;
643 os.fill('\0');
644 memcpy(os.data(), challenge->os, sizeof(challenge->os));
645 _os = os.data();
646
647 // Restore string order as its byte order is reversed
648 std::reverse(_os.begin(), _os.end());
649
650 _localizationName.resize(4);
651 for (int i = 0; i < 4; ++i)
652 _localizationName[i] = challenge->country[4 - i - 1];
653
654 // Get the account details from the account table
656 stmt->SetData(0, GetRemoteIpAddress().to_string());
657 stmt->SetData(1, login);
658
659 _queryProcessor.AddCallback(LoginDatabase.AsyncQuery(stmt).WithPreparedCallback(std::bind(&AuthSession::ReconnectChallengeCallback, this, std::placeholders::_1)));
660 return true;
661}
@ LOGIN_SEL_RECONNECTCHALLENGE
Definition LoginDatabase.h:45
void ReconnectChallengeCallback(PreparedQueryResult result)
Definition AuthSession.cpp:663

References _build, _expversion, _localizationName, _os, _queryProcessor, _status, AsyncCallbackProcessor< T >::AddCallback(), AUTH_LOGON_CHALLENGE_INITIAL_SIZE, AUTH_LOGON_CHALLENGE_C::build, AUTH_LOGON_CHALLENGE_C::country, Socket< AuthSession >::GetReadBuffer(), MessageBuffer::GetReadPointer(), Socket< AuthSession >::GetRemoteIpAddress(), AUTH_LOGON_CHALLENGE_C::I, AUTH_LOGON_CHALLENGE_C::I_len, AuthHelper::IsPostBCAcceptedClientBuild(), AuthHelper::IsPreBCAcceptedClientBuild(), LOG_DEBUG, LOGIN_SEL_RECONNECTCHALLENGE, LoginDatabase, NO_VALID_EXP_FLAG, AUTH_LOGON_CHALLENGE_C::os, POST_BC_EXP_FLAG, PRE_BC_EXP_FLAG, ReconnectChallengeCallback(), PreparedStatementBase::SetData(), AUTH_LOGON_CHALLENGE_C::size, and STATUS_CLOSED.

Referenced by InitHandlers().

◆ HandleReconnectProof()

bool AuthSession::HandleReconnectProof ( )
private
690{
691 LOG_DEBUG("server.authserver", "Entering _HandleReconnectProof");
693
694 sAuthReconnectProof_C* reconnectProof = reinterpret_cast<sAuthReconnectProof_C*>(GetReadBuffer().GetReadPointer());
695
696 if (_accountInfo.Login.empty())
697 return false;
698
701 sha.UpdateData(reconnectProof->R1, 16);
704 sha.Finalize();
705
706 if (sha.GetDigest() == reconnectProof->R2)
707 {
708 if (!VerifyVersion(reconnectProof->R1, sizeof(reconnectProof->R1), reconnectProof->R3, true))
709 {
710 ByteBuffer packet;
711 packet << uint8(AUTH_RECONNECT_PROOF);
713 SendPacket(packet);
714 return true;
715 }
716
717 // Sending response
718 ByteBuffer pkt;
720 pkt << uint8(WOW_SUCCESS);
721 pkt << uint16(0); // LoginFlags, 1 has account message
722 SendPacket(pkt);
724 return true;
725 }
726 else
727 {
728 LOG_ERROR("server.authserver.hack", "'{}:{}' [ERROR] user {} tried to login, but session is invalid.", GetRemoteIpAddress().to_string(),
730 return false;
731 }
732}
@ WOW_SUCCESS
Definition AuthCodes.h:25
@ AUTH_RECONNECT_PROOF
Definition AuthSession.cpp:44
#define LOG_ERROR(filterType__,...)
Definition Log.h:145
Definition CryptoHash.h:43
void Finalize()
Definition CryptoHash.h:123
void UpdateData(uint8 const *data, std::size_t len)
Definition CryptoHash.h:110
Digest const & GetDigest() const
Definition CryptoHash.h:131
std::array< uint8, 16 > _reconnectProof
Definition AuthSession.h:97
Definition AuthSession.cpp:107
uint8 R1[16]
Definition AuthSession.cpp:109
Acore::Crypto::SHA1::Digest R2
Definition AuthSession.cpp:110
Acore::Crypto::SHA1::Digest R3
Definition AuthSession.cpp:110

References _accountInfo, _reconnectProof, _sessionKey, _status, AUTH_RECONNECT_PROOF, Acore::Impl::GenericHash< HashCreator, DigestLength >::Finalize(), Acore::Impl::GenericHash< HashCreator, DigestLength >::GetDigest(), Socket< AuthSession >::GetReadBuffer(), MessageBuffer::GetReadPointer(), Socket< AuthSession >::GetRemoteIpAddress(), Socket< AuthSession >::GetRemotePort(), LOG_DEBUG, LOG_ERROR, AccountInfo::Login, AUTH_RECONNECT_PROOF_C::R1, AUTH_RECONNECT_PROOF_C::R2, AUTH_RECONNECT_PROOF_C::R3, SendPacket(), STATUS_AUTHED, STATUS_CLOSED, Acore::Impl::GenericHash< HashCreator, DigestLength >::UpdateData(), VerifyVersion(), WOW_FAIL_VERSION_INVALID, and WOW_SUCCESS.

Referenced by InitHandlers().

◆ InitHandlers()

std::unordered_map< uint8, AuthHandler > AuthSession::InitHandlers ( )
static
125{
126 std::unordered_map<uint8, AuthHandler> handlers;
127
133
134 return handlers;
135}
@ REALM_LIST
Definition AuthSession.cpp:45
@ AUTH_RECONNECT_CHALLENGE
Definition AuthSession.cpp:43
#define REALM_LIST_PACKET_SIZE
Definition AuthSession.cpp:122
@ STATUS_RECONNECT_PROOF
Definition AuthSession.h:41
@ STATUS_LOGON_PROOF
Definition AuthSession.h:40
bool HandleLogonChallenge()
Definition AuthSession.cpp:286
bool HandleLogonProof()
Definition AuthSession.cpp:464
bool HandleReconnectChallenge()
Definition AuthSession.cpp:628
bool HandleRealmList()
Definition AuthSession.cpp:734
bool HandleReconnectProof()
Definition AuthSession.cpp:689

References AUTH_LOGON_CHALLENGE, AUTH_LOGON_CHALLENGE_INITIAL_SIZE, AUTH_LOGON_PROOF, AUTH_RECONNECT_CHALLENGE, AUTH_RECONNECT_PROOF, HandleLogonChallenge(), HandleLogonProof(), HandleRealmList(), HandleReconnectChallenge(), HandleReconnectProof(), REALM_LIST, REALM_LIST_PACKET_SIZE, STATUS_AUTHED, STATUS_CHALLENGE, STATUS_LOGON_PROOF, and STATUS_RECONNECT_PROOF.

◆ LogonChallengeCallback()

void AuthSession::LogonChallengeCallback ( PreparedQueryResult  result)
private
326{
327 ByteBuffer pkt;
329 pkt << uint8(0x00);
330
331 if (!result)
332 {
334 SendPacket(pkt);
335 return;
336 }
337
338 Field* fields = result->Fetch();
339
340 _accountInfo.LoadResult(fields);
341
342 std::string ipAddress = GetRemoteIpAddress().to_string();
343 uint16 port = GetRemotePort();
344
345 // If the IP is 'locked', check that the player comes indeed from the correct IP address
347 {
348 LOG_DEBUG("server.authserver", "[AuthChallenge] Account '{}' is locked to IP - '{}' is logging in from '{}'", _accountInfo.Login, _accountInfo.LastIP, ipAddress);
349 if (_accountInfo.LastIP != ipAddress)
350 {
352 SendPacket(pkt);
353 return;
354 }
355 }
356 else
357 {
358 if (IpLocationRecord const* location = sIPLocation->GetLocationRecord(ipAddress))
359 _ipCountry = location->CountryCode;
360
361 LOG_DEBUG("server.authserver", "[AuthChallenge] Account '{}' is not locked to ip", _accountInfo.Login);
362 if (_accountInfo.LockCountry.empty() || _accountInfo.LockCountry == "00")
363 LOG_DEBUG("server.authserver", "[AuthChallenge] Account '{}' is not locked to country", _accountInfo.Login);
364 else if (!_ipCountry.empty())
365 {
366 LOG_DEBUG("server.authserver", "[AuthChallenge] Account '{}' is locked to country: '{}' Player country is '{}'", _accountInfo.Login, _accountInfo.LockCountry, _ipCountry);
368 {
370 SendPacket(pkt);
371 return;
372 }
373 }
374 }
375
376 // If the account is banned, reject the logon attempt
378 {
380 {
381 pkt << uint8(WOW_FAIL_BANNED);
382 SendPacket(pkt);
383 LOG_INFO("server.authserver.banned", "'{}:{}' [AuthChallenge] Banned account {} tried to login!", ipAddress, port, _accountInfo.Login);
384 return;
385 }
386 else
387 {
389 SendPacket(pkt);
390 LOG_INFO("server.authserver.banned", "'{}:{}' [AuthChallenge] Temporarily banned account {} tried to login!", ipAddress, port, _accountInfo.Login);
391 return;
392 }
393 }
394
395 uint8 securityFlags = 0;
396
397 // Check if a TOTP token is needed
398 if (!fields[12].IsNull())
399 {
400 securityFlags = 4;
401 _totpSecret = fields[12].Get<Binary>();
402
403 if (auto const& secret = sSecretMgr->GetSecret(SECRET_TOTP_MASTER_KEY))
404 {
405 bool success = Acore::Crypto::AEDecrypt<Acore::Crypto::AES>(*_totpSecret, *secret);
406 if (!success)
407 {
408 pkt << uint8(WOW_FAIL_DB_BUSY);
409 LOG_ERROR("server.authserver", "[AuthChallenge] Account '{}' has invalid ciphertext for TOTP token key stored", _accountInfo.Login);
410 SendPacket(pkt);
411 return;
412 }
413 }
414 }
415
416 _srp6.emplace(_accountInfo.Login,
417 fields[13].Get<Binary, Acore::Crypto::SRP6::SALT_LENGTH>(),
419
420 // Fill the response packet with the result
422 {
423 pkt << uint8(WOW_SUCCESS);
424
425 pkt.append(_srp6->B);
426 pkt << uint8(1);
427 pkt.append(_srp6->g);
428 pkt << uint8(32);
429 pkt.append(_srp6->N);
430 pkt.append(_srp6->s);
431 pkt.append(VersionChallenge.data(), VersionChallenge.size());
432 pkt << uint8(securityFlags); // security flags (0x0...0x04)
433
434 if (securityFlags & 0x01) // PIN input
435 {
436 pkt << uint32(0);
437 pkt << uint64(0) << uint64(0); // 16 bytes hash?
438 }
439
440 if (securityFlags & 0x02) // Matrix input
441 {
442 pkt << uint8(0);
443 pkt << uint8(0);
444 pkt << uint8(0);
445 pkt << uint8(0);
446 pkt << uint64(0);
447 }
448
449 if (securityFlags & 0x04) // Security token input
450 pkt << uint8(1);
451
452 LOG_DEBUG("server.authserver", "'{}:{}' [AuthChallenge] account {} is using '{}' locale",
453 ipAddress, port, _accountInfo.Login, _localizationName);
454
456 }
457 else
459
460 SendPacket(pkt);
461}
@ WOW_FAIL_LOCKED_ENFORCED
Definition AuthCodes.h:39
@ WOW_FAIL_SUSPENDED
Definition AuthCodes.h:35
@ WOW_FAIL_DB_BUSY
Definition AuthCodes.h:31
@ WOW_FAIL_UNLOCKABLE_LOCK
Definition AuthCodes.h:48
std::array< uint8, 16 > VersionChallenge
Definition AuthSession.cpp:117
std::uint64_t uint64
Definition Define.h:106
std::vector< uint8 > Binary
Definition Field.h:41
#define sIPLocation
Definition IPLocation.h:49
#define sSecretMgr
Definition SecretMgr.h:72
@ SECRET_TOTP_MASTER_KEY
Definition SecretMgr.h:30
static constexpr std::size_t VERIFIER_LENGTH
Definition SRP6.h:34
static constexpr std::size_t SALT_LENGTH
Definition SRP6.h:31
std::string _ipCountry
Definition AuthSession.h:104
void append(T value)
Definition ByteBuffer.h:129
Class used to access individual fields of database query result.
Definition Field.h:99
std::enable_if_t< std::is_arithmetic_v< T >, T > Get() const
Definition Field.h:113
bool IsAcceptedClientBuild(uint32 build)
Definition AuthCodes.cpp:35
std::string LockCountry
Definition AuthSession.h:55
bool IsPermanentlyBanned
Definition AuthSession.h:60
void LoadResult(Field *fields)
Definition AuthSession.cpp:139
bool IsBanned
Definition AuthSession.h:59
bool IsLockedToIP
Definition AuthSession.h:54
std::string LastIP
Definition AuthSession.h:56
Definition IPLocation.h:23

References _accountInfo, _build, _ipCountry, _localizationName, _srp6, _status, _totpSecret, ByteBuffer::append(), AUTH_LOGON_CHALLENGE, Field::Get(), Socket< AuthSession >::GetRemoteIpAddress(), Socket< AuthSession >::GetRemotePort(), AuthHelper::IsAcceptedClientBuild(), AccountInfo::IsBanned, AccountInfo::IsLockedToIP, AccountInfo::IsPermanentlyBanned, AccountInfo::LastIP, AccountInfo::LoadResult(), AccountInfo::LockCountry, LOG_DEBUG, LOG_ERROR, LOG_INFO, AccountInfo::Login, Acore::Crypto::SRP6::SALT_LENGTH, SECRET_TOTP_MASTER_KEY, SendPacket(), sIPLocation, sSecretMgr, STATUS_LOGON_PROOF, Acore::Crypto::SRP6::VERIFIER_LENGTH, VersionChallenge, WOW_FAIL_BANNED, WOW_FAIL_DB_BUSY, WOW_FAIL_LOCKED_ENFORCED, WOW_FAIL_SUSPENDED, WOW_FAIL_UNKNOWN_ACCOUNT, WOW_FAIL_UNLOCKABLE_LOCK, WOW_FAIL_VERSION_INVALID, and WOW_SUCCESS.

Referenced by HandleLogonChallenge().

◆ ReadHandler()

SocketReadCallbackResult AuthSession::ReadHandler ( )
finalprotectedvirtual

Implements Socket< AuthSession >.

223{
224 MessageBuffer& packet = GetReadBuffer();
225
226 while (packet.GetActiveSize())
227 {
228 uint8 cmd = packet.GetReadPointer()[0];
229 auto itr = Handlers.find(cmd);
230 if (itr == Handlers.end())
231 {
232 // well we dont handle this, lets just ignore it
233 packet.Reset();
234 break;
235 }
236
237 if (_status != itr->second.status)
238 {
239 CloseSocket();
241 }
242
243 uint16 size = uint16(itr->second.packetSize);
244 if (packet.GetActiveSize() < size)
245 break;
246
248 {
249 sAuthLogonChallenge_C* challenge = reinterpret_cast<sAuthLogonChallenge_C*>(packet.GetReadPointer());
250 size += challenge->size;
252 {
253 CloseSocket();
255 }
256 }
257
258 if (packet.GetActiveSize() < size)
259 break;
260
261 if (!(*this.*itr->second.handler)())
262 {
263 CloseSocket();
265 }
266
267 packet.ReadCompleted(size);
268 }
269
271}
#define MAX_ACCEPTED_CHALLENGE_SIZE
Definition AuthSession.cpp:119
std::unordered_map< uint8, AuthHandler > const Handlers
Definition AuthSession.cpp:137
Definition MessageBuffer.h:26
size_type GetActiveSize() const
Definition MessageBuffer.h:64
void Reset()
Definition MessageBuffer.h:46
void CloseSocket()
Definition Socket.h:172

References _status, AUTH_LOGON_CHALLENGE, AUTH_RECONNECT_CHALLENGE, Socket< AuthSession >::CloseSocket(), MessageBuffer::GetActiveSize(), Socket< AuthSession >::GetReadBuffer(), MessageBuffer::GetReadPointer(), Handlers, KeepReading, MAX_ACCEPTED_CHALLENGE_SIZE, MessageBuffer::ReadCompleted(), MessageBuffer::Reset(), AUTH_LOGON_CHALLENGE_C::size, and Stop.

◆ RealmListCallback()

void AuthSession::RealmListCallback ( PreparedQueryResult  result)
private
747{
748 std::map<uint32, uint8> characterCounts;
749 if (result)
750 {
751 do
752 {
753 Field* fields = result->Fetch();
754 characterCounts[fields[0].Get<uint32>()] = fields[1].Get<uint8>();
755 } while (result->NextRow());
756 }
757
758 // Circle through realms in the RealmList and construct the return packet (including # of user characters in each realm)
759 ByteBuffer pkt;
760
761 std::size_t RealmListSize = 0;
762 for (auto const& [realmHandle, realm] : sRealmList->GetRealms())
763 {
764 // don't work with realms which not compatible with the client
766
767 // No SQL injection. id of realm is controlled by the database.
768 uint32 flag = realm.Flags;
769 RealmBuildInfo const* buildInfo = sRealmList->GetBuildInfo(realm.Build);
770 if (!okBuild)
771 {
772 if (!buildInfo)
773 continue;
774
775 flag |= REALM_FLAG_OFFLINE | REALM_FLAG_SPECIFYBUILD; // tell the client what build the realm is for
776 }
777
778 if (!buildInfo)
779 flag &= ~REALM_FLAG_SPECIFYBUILD;
780
781 std::string name = realm.Name;
783 {
784 std::ostringstream ss;
785 ss << name << " (" << buildInfo->MajorVersion << '.' << buildInfo->MinorVersion << '.' << buildInfo->BugfixVersion << ')';
786 name = ss.str();
787 }
788
790
791 pkt << uint8(realm.Type); // realm type
792 if (_expversion & POST_BC_EXP_FLAG) // only 2.x and 3.x clients
793 pkt << uint8(lock); // if 1, then realm locked
794
795 pkt << uint8(flag); // RealmFlags
796 pkt << name;
797 pkt << boost::lexical_cast<std::string>(realm.GetAddressForClient(GetRemoteIpAddress()));
798 pkt << float(realm.PopulationLevel);
799 pkt << uint8(characterCounts[realm.Id.Realm]);
800 pkt << uint8(realm.Timezone); // realm category
801
802 if (_expversion & POST_BC_EXP_FLAG) // 2.x and 3.x clients
803 pkt << uint8(realm.Id.Realm);
804 else
805 pkt << uint8(0x0); // 1.12.1 and 1.12.2 clients
806
808 {
809 pkt << uint8(buildInfo->MajorVersion);
810 pkt << uint8(buildInfo->MinorVersion);
811 pkt << uint8(buildInfo->BugfixVersion);
812 pkt << uint16(buildInfo->Build);
813 }
814
815 ++RealmListSize;
816 }
817
818 if (_expversion & POST_BC_EXP_FLAG) // 2.x and 3.x clients
819 {
820 pkt << uint8(0x10);
821 pkt << uint8(0x00);
822 }
823 else // 1.12.1 and 1.12.2 clients
824 {
825 pkt << uint8(0x00);
826 pkt << uint8(0x02);
827 }
828
829 // make a ByteBuffer which stores the RealmList's size
830 ByteBuffer RealmListSizeBuffer;
831 RealmListSizeBuffer << uint32(0);
832
833 if (_expversion & POST_BC_EXP_FLAG) // only 2.x and 3.x clients
834 RealmListSizeBuffer << uint16(RealmListSize);
835 else
836 RealmListSizeBuffer << uint32(RealmListSize);
837
838 ByteBuffer hdr;
839 hdr << uint8(REALM_LIST);
840 hdr << uint16(pkt.size() + RealmListSizeBuffer.size());
841 hdr.append(RealmListSizeBuffer); // append RealmList's size buffer
842 hdr.append(pkt); // append realms in the realmlist
843 SendPacket(hdr);
844
846}
#define sRealmList
Definition RealmList.h:83
@ REALM_FLAG_OFFLINE
Definition Realm.h:29
@ REALM_FLAG_SPECIFYBUILD
Definition Realm.h:30
std::size_t size() const
Definition ByteBuffer.h:444
Realm realm
Definition World.cpp:117
AccountTypes SecurityLevel
Definition AuthSession.h:61
Definition RealmList.h:40
uint32 MajorVersion
Definition RealmList.h:42
uint32 BugfixVersion
Definition RealmList.h:44
uint32 Build
Definition RealmList.h:41
uint32 MinorVersion
Definition RealmList.h:43
uint32 Realm
Definition Realm.h:43
RealmFlags Flags
Definition Realm.h:77
AccountTypes AllowedSecurityLevel
Definition Realm.h:79
boost::asio::ip::tcp_endpoint GetAddressForClient(boost::asio::ip::address const &clientAddr) const
Definition Realm.cpp:23
uint8 Timezone
Definition Realm.h:78
float PopulationLevel
Definition Realm.h:80
uint32 Build
Definition Realm.h:70
std::string Name
Definition Realm.h:75
RealmHandle Id
Definition Realm.h:69
uint8 Type
Definition Realm.h:76

References _accountInfo, _build, _expversion, _status, Realm::AllowedSecurityLevel, ByteBuffer::append(), RealmBuildInfo::BugfixVersion, Realm::Build, RealmBuildInfo::Build, Realm::Flags, Field::Get(), Realm::GetAddressForClient(), Socket< AuthSession >::GetRemoteIpAddress(), Realm::Id, AuthHelper::IsPreBCAcceptedClientBuild(), RealmBuildInfo::MajorVersion, RealmBuildInfo::MinorVersion, Realm::Name, Realm::PopulationLevel, POST_BC_EXP_FLAG, PRE_BC_EXP_FLAG, realm, RealmHandle::Realm, REALM_FLAG_OFFLINE, REALM_FLAG_SPECIFYBUILD, REALM_LIST, AccountInfo::SecurityLevel, SendPacket(), ByteBuffer::size(), sRealmList, STATUS_AUTHED, Realm::Timezone, and Realm::Type.

Referenced by HandleRealmList().

◆ ReconnectChallengeCallback()

void AuthSession::ReconnectChallengeCallback ( PreparedQueryResult  result)
private
664{
665 ByteBuffer pkt;
667
668 if (!result)
669 {
671 SendPacket(pkt);
672 return;
673 }
674
675 Field* fields = result->Fetch();
676
677 _accountInfo.LoadResult(fields);
678 _sessionKey = fields[12].Get<Binary, SESSION_KEY_LENGTH>();
681
682 pkt << uint8(WOW_SUCCESS);
684 pkt.append(VersionChallenge.data(), VersionChallenge.size());
685
686 SendPacket(pkt);
687}
constexpr std::size_t SESSION_KEY_LENGTH
Definition AuthDefines.h:24
std::array< uint8, S > GetRandomBytes()
Definition CryptoRandom.h:35

References _accountInfo, _reconnectProof, _sessionKey, _status, ByteBuffer::append(), AUTH_RECONNECT_CHALLENGE, Field::Get(), Acore::Crypto::GetRandomBytes(), AccountInfo::LoadResult(), SendPacket(), SESSION_KEY_LENGTH, STATUS_RECONNECT_PROOF, VersionChallenge, WOW_FAIL_UNKNOWN_ACCOUNT, and WOW_SUCCESS.

Referenced by HandleReconnectChallenge().

◆ SendPacket()

void AuthSession::SendPacket ( ByteBuffer &  packet)
274{
275 if (!IsOpen())
276 return;
277
278 if (!packet.empty())
279 {
280 MessageBuffer buffer(packet.size());
281 buffer.Write(packet.contents(), packet.size());
282 QueuePacket(std::move(buffer));
283 }
284}
bool empty() const
Definition ByteBuffer.h:445
uint8 * contents()
Definition ByteBuffer.h:424
void QueuePacket(MessageBuffer &&buffer)
Definition Socket.h:159
bool IsOpen() const
Definition Socket.h:170

References ByteBuffer::contents(), ByteBuffer::empty(), Socket< AuthSession >::IsOpen(), Socket< AuthSession >::QueuePacket(), ByteBuffer::size(), and MessageBuffer::Write().

Referenced by CheckIpCallback(), HandleLogonProof(), HandleReconnectProof(), LogonChallengeCallback(), RealmListCallback(), and ReconnectChallengeCallback().

◆ Start()

void AuthSession::Start ( )
overridevirtual

Implements Socket< AuthSession >.

172{
173 std::string ip_address = GetRemoteIpAddress().to_string();
174 LOG_TRACE("session", "Accepted connection from {}", ip_address);
175
177 stmt->SetData(0, ip_address);
178
179 _queryProcessor.AddCallback(LoginDatabase.AsyncQuery(stmt).WithPreparedCallback(std::bind(&AuthSession::CheckIpCallback, this, std::placeholders::_1)));
180}
#define LOG_TRACE(filterType__,...)
Definition Log.h:161
@ LOGIN_SEL_IP_INFO
Definition LoginDatabase.h:34
void CheckIpCallback(PreparedQueryResult result)
Definition AuthSession.cpp:192

References _queryProcessor, AsyncCallbackProcessor< T >::AddCallback(), CheckIpCallback(), Socket< AuthSession >::GetRemoteIpAddress(), LOG_TRACE, LOGIN_SEL_IP_INFO, LoginDatabase, and PreparedStatementBase::SetData().

◆ Update()

bool AuthSession::Update ( )
finalvirtual

Reimplemented from Socket< AuthSession >.

183{
184 if (!AuthSocket::Update())
185 return false;
186
188
189 return true;
190}
void ProcessReadyCallbacks()
Definition AsyncCallbackProcessor.h:40
virtual bool Update()
Definition Socket.h:86

References _queryProcessor, AsyncCallbackProcessor< T >::ProcessReadyCallbacks(), and Socket< AuthSession >::Update().

◆ VerifyVersion()

bool AuthSession::VerifyVersion ( uint8 const *  a,
int32  aLength,
Acore::Crypto::SHA1::Digest const &  versionProof,
bool  isReconnect 
)
private
849{
850 if (!sConfigMgr->GetOption<bool>("StrictVersionCheck", false))
851 return true;
852
854 Acore::Crypto::SHA1::Digest const* versionHash{ nullptr };
855
856 if (!isReconnect)
857 {
858 RealmBuildInfo const* buildInfo = sRealmList->GetBuildInfo(_build);
859 if (!buildInfo)
860 return false;
861
862 if (_os == "Win")
863 versionHash = &buildInfo->WindowsHash;
864 else if (_os == "OSX")
865 versionHash = &buildInfo->MacHash;
866
867 if (!versionHash)
868 return false;
869
870 if (zeros == *versionHash)
871 return true; // not filled serverside
872 }
873 else
874 versionHash = &zeros;
875
876 Acore::Crypto::SHA1 version;
877 version.UpdateData(a, aLength);
878 version.UpdateData(*versionHash);
879 version.Finalize();
880
881 return (versionProof == version.GetDigest());
882}
std::array< uint8, DIGEST_LENGTH > Digest
Definition CryptoHash.h:46
std::array< uint8, 20 > WindowsHash
Definition RealmList.h:46
std::array< uint8, 20 > MacHash
Definition RealmList.h:47

References _build, _os, Acore::Impl::GenericHash< HashCreator, DigestLength >::Finalize(), Acore::Impl::GenericHash< HashCreator, DigestLength >::GetDigest(), RealmBuildInfo::MacHash, sConfigMgr, sRealmList, Acore::Impl::GenericHash< HashCreator, DigestLength >::UpdateData(), and RealmBuildInfo::WindowsHash.

Referenced by HandleLogonProof(), and HandleReconnectProof().

Member Data Documentation

◆ _accountInfo

◆ _build

◆ _expversion

uint8 AuthSession::_expversion
private

◆ _ipCountry

std::string AuthSession::_ipCountry
private

Referenced by LogonChallengeCallback().

◆ _localizationName

std::string AuthSession::_localizationName
private

◆ _os

std::string AuthSession::_os
private

◆ _queryProcessor

◆ _reconnectProof

std::array<uint8, 16> AuthSession::_reconnectProof = {}
private

◆ _sessionKey

SessionKey AuthSession::_sessionKey = {}
private

◆ _srp6

Optional<Acore::Crypto::SRP6> AuthSession::_srp6
private

◆ _status

◆ _totpSecret

Optional<std::vector<uint8> > AuthSession::_totpSecret
private

The documentation for this class was generated from the following files: